

C3PAO assessments are paused. Your CMMC requirements are not.
Get CMMC trained by the experts who run the assessments.
When the assessment phase paused, the DFARS requirements didn't move. NIST SP 800-171 still applies to every contract that carries it, and DIBCAC is still conducting government-led assessments. This training gets your team ready now, so the pause buys you preparation time instead of a false sense of relief.
Ready to get trained?
Built for the people meeting the requirements, not certifying against them
CCP and CCA courses exist to certify assessors. They're dense, expensive, and taught by instructors who've never looked at your systems. This is for the IT and security staff and compliance leads inside DIB companies who carry the actual work - implementing controls, writing POA&Ms, and standing behind their documentation when a real assessment comes. You get what applies to you, and nothing you'll never use.
5 full days that prepares you for CMMC.
We start with scoping. Before a single control matters, you have to know what's in scope - which systems, which data, which people. We teach you how to draw those boundaries correctly, because a wrong scope is the fastest way to fail an assessment or overspend protecting things that don't need it.
Step 1
Step 2
We cover every control, one at a time. All 110 controls in NIST SP 800-171 and the assessment objectives behind them. Not a skim - the level of detail an assessor actually evaluates you against, so nothing on assessment day is unfamiliar.
We give you reference architectures that meet the controls. Knowing what a control requires and knowing how to build for it are different problems. We provide actionable reference architectures your team can apply to your own environment, so you leave with a path to implementation, not just a list of requirements.
Step 3
Step 4
You finish “ready to get ready.” By the end, your team understands scoping, every control and objective, and how to build toward them - fully prepared to run your own readiness work and walk into an assessment knowing what to expect.

FAQs
-
Our CMMC training for the DIB runs Monday-Friday from 10am-4pm ET every day with a built in hour long lunch break.
-
The training is delivered virtually with plenty of room for questions from your team - so bring them all!
-
You don’t have to be a an IT person to benefit from our training. CMMC impacts everyone at your company - from leadership, to procurement, to HR - so bring everyone!
-
Yes! Please email us at accountsreceivable [at] hivesystems.com and we’ll send you an invoice instead.

Taught by assessors, not academics
We're a C3PAO. Our team has assessed defense contractors and walked them through getting ready for real - that's the gap between knowing what the requirements say and knowing what it takes to pass. Because sessions are live and virtual, your team can ask questions, get straight answers, and apply them to your own environment while we're in the room.
Small business? You pay less.
Defense contracts don't only go to large primes, and neither does this training. If you qualify as a small business under any SBA socioeconomic category - woman-owned, service-disabled veteran-owned, HUBZone, 8(a), and more - you get 50% off. Same live sessions, same assessors, same readiness - built for the smaller shops that carry a real share of the Defense Industrial Base and feel every compliance cost more sharply. Have your designation handy when you register and the discount applies at checkout.
Upskill your CMMC knowledge.

Understand where you stand.
Access our FREE CMMC Level 2 Assessment Tool to complete your CMMC Level 2 self assessment. Our free tool will walk you through all the parts of your assessment to obtain your CMMC required SPRS score and identify areas for improvement and gaps prior to engaging a C3PAO
Jump start your paperwork.
Our comprehensive CMMC SSP templates to help you build your CMMC-compliant System Security Plan (SSP) using NIST 800-171 Rev. 2, or prepare for the future with NIST 800-171 Rev. 3.
Inheriting controls from a FedRAMP provider?
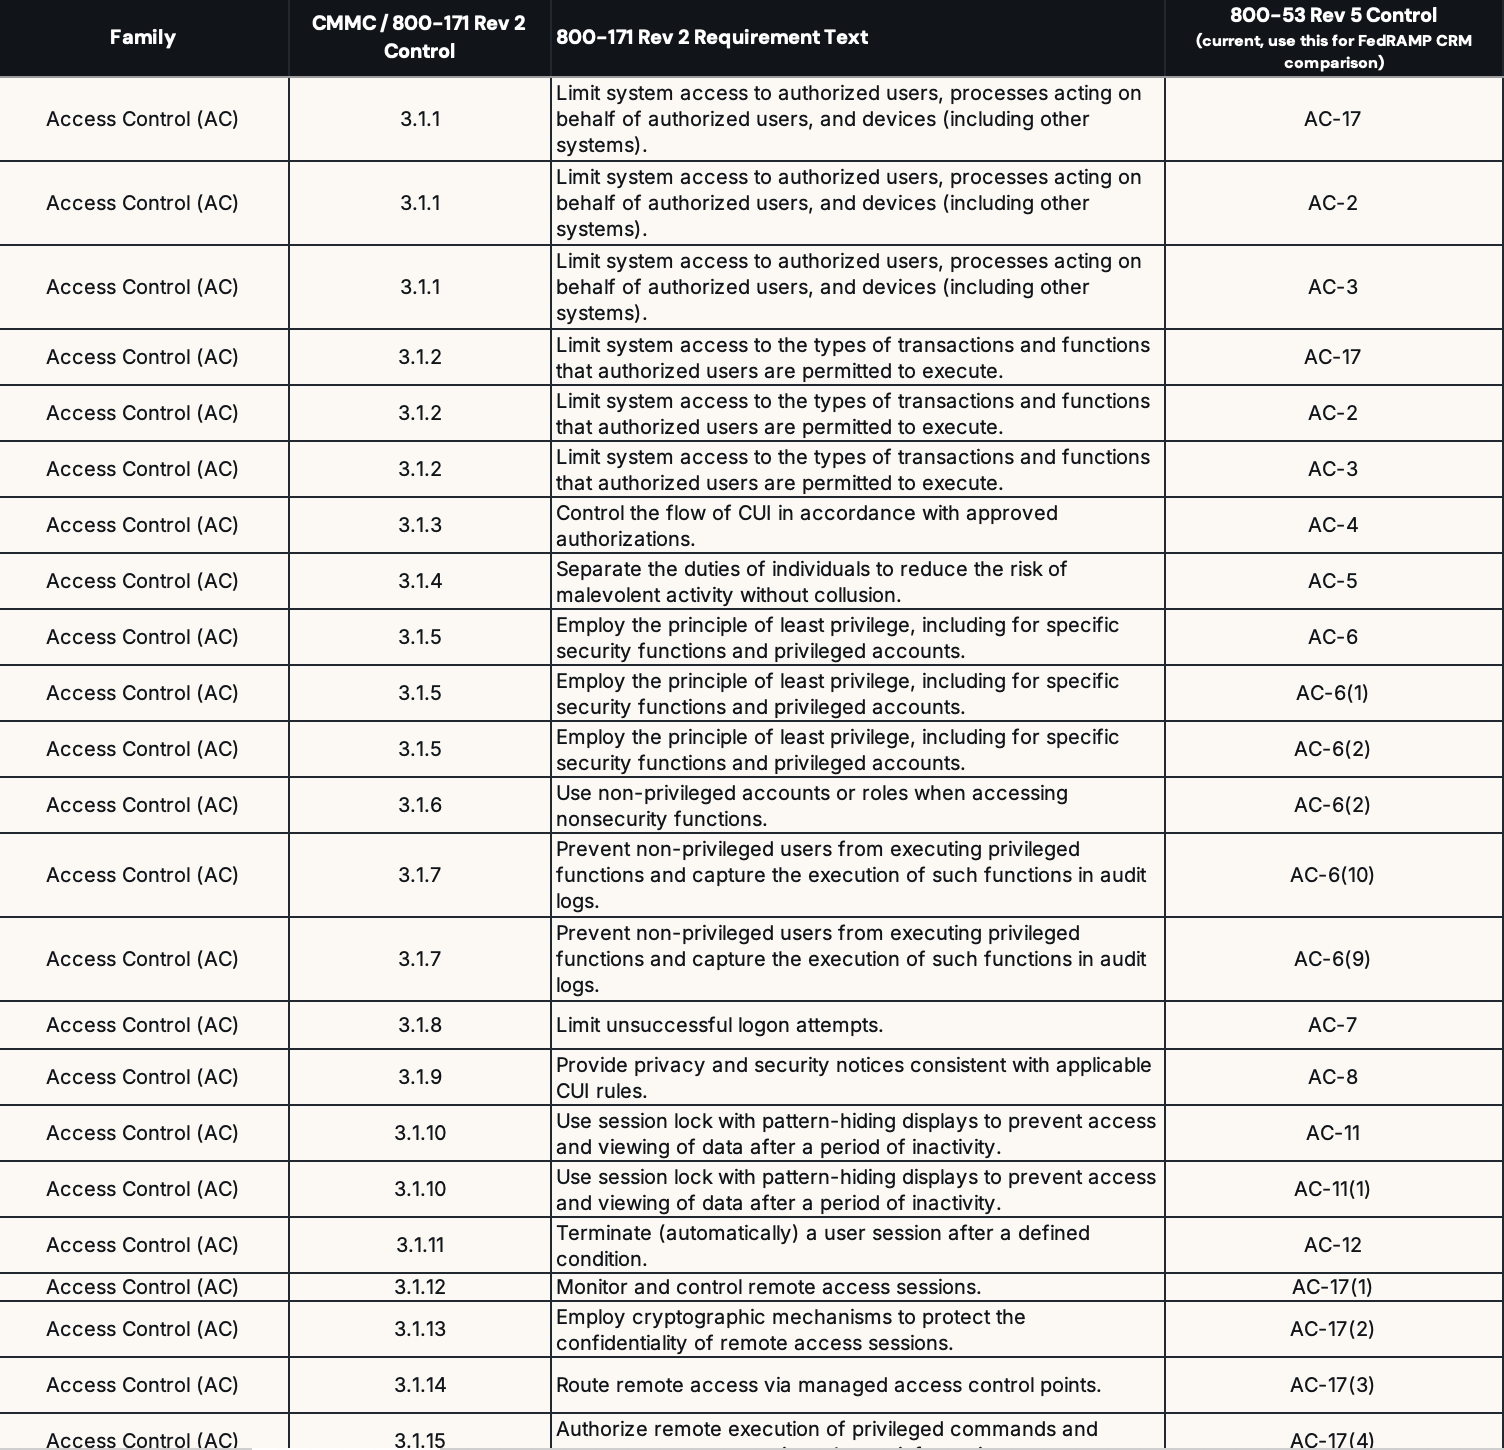
Our free NIST 800-171 Rev 2 to 800-53 Rev 5 Crosswalk maps all 110 CMMC Level 2 requirements to their current 800-53 Rev 5 controls, so you can line your assessment up against a provider's Customer Responsibility Matrix and see exactly what you can inherit.

Ready to take the next step?
Talk to an expert about CMMC, our services, pricing, or anything else.
Contact us about CMMC ❯